Active Deception: The Game-Changing Strategy CISOs Need for IT/OT Security
Blog / 4 min read
In today’s AI-powered threat landscape, traditional perimeter defenses are no longer enough. Sophisticated attackers use automation, polymorphic malware, and advanced reconnaissance to bypass firewalls and signature-based security tools with ease. This blog post discusses the multiple advantages of using an integrated cybersecurity solution, as well as its effectiveness in combating changing cyber threats.
For CISOs, SOC leaders, and OT security heads, the biggest problem is clear: most security tools are static and predictable - making them easy for attackers to fingerprint, evade, and ignore.
The solution?
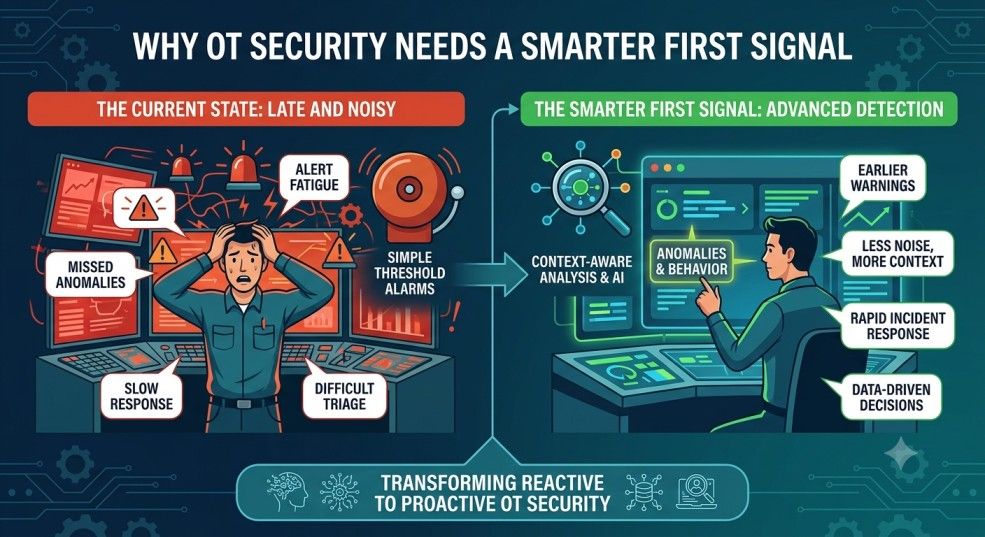
A fundamental shift from reactive detection to proactive, dynamic active deception - technology that doesn’t just wait for attackers but actively lures and traps them.
The Evolution of Deception Technology: From Static Honeypots to Adaptive Defense
Traditional honeypots have been used for years as decoys to attract and study attackers. While useful, skilled adversaries quickly identify and helps to avoid these static traps.
Modern active deception technology goes far beyond legacy honeypots. Next-generation platforms leverage automation, AI-driven analytics, and dynamic environment generation to create shifting, dynamic decoys that continuously evolve their signatures, behavior, and network footprint.
This evolution delivers greater stealth, resilience, and long-term effectiveness - turning deception into a living, adaptive defensive layer that evolves with the threat landscape.
Introducing ZeroHack TRACE: Deception-Powered Threat Intelligence
ZeroHack TRACE from WhizHack is a sovereign, Made-in-India cybersecurity solution designed for both enterprise IT and critical Operational Technology (OT) environments.
It includes:
- ZeroHack TRACE - for data centres, corporate networks, cloud, and hybrid IT setups
- ZeroHack TRACE OT - for industrial control systems, SCADA, PLCs, and air-gapped networks
TRACE deploys highly realistic decoys that mimic high-value assets - servers, databases, PLCs, HMIs, and SCADA systems - to lure attackers away from production environments and into controlled deception layers.
Every interaction with these decoys generates high-fidelity threat intelligence that traditional tools simply cannot match.
The DISS® Advantage: Dynamic, Intelligent, and Unpredictable Defense
At the core of ZeroHack TRACE lies WhizHack’s proprietary Dynamic Intelligent Shifting Sensors (DISS®) technology.
DISS® sensors are intelligently deployed across DMZ, internal networks, external network, and industrial zones. These sensors periodically shift their position, configuration, and behavior - making them extremely difficult for attackers to fingerprint or map accurately.
Instead of static traps, DISS® creates a dynamic deception surface that keeps adversaries constantly guessing while feeding your threat intelligence engine with fresh, actionable data.
Proven Benefits of Active Deception Technology
Organizations deploying Active Deception Technology report measurable improvements in threat detection, response, and operational efficiency:
- Detecting attackers during reconnaissance and lateral movement stages can reduce breach identification time by up to 50%, enabling faster containment and response. (Source: IBM X-Force Threat Intelligence Index 2023)
- Organizations adopting deception report investigation time reductions of 40–60%, faster containment...and fewer false positives.
- Rapid detection and actionable intelligence can improve incident response efficiency by up to 60%, minimizing operational disruption and potential damage. (Source: FireEye Report)
- Machine learning-driven deception strategies improve adaptability, leading to better resilience against new attack vectors. (Gartner preemptive cybersecurity insights)
Why ZeroHack TRACE Stands Out?
Domain-Specific Honeynets
TRACE builds highly realistic, environment-specific honeynets that mimic your actual IT and OT assets - from enterprise applications and databases to PLCs and SCADA systems. Every engagement becomes inherently suspicious.
Raw Deep Packet Inspection (DPI) & Real Threat Data
Each sensor includes a powerful DPI engine that captures complete attack payloads, tools, and TTPs in real time - delivering more realistic data for threat hunting and SOC enrichment.
Self-Healing, Auto-Updating & Reconfigurable Sensors
Sensors automatically heal after attacks, auto-update, and reconfigure to match evolving network changes - significantly reducing maintenance overhead.
Purpose-Built for OT and Air-Gapped Environments
TRACE OT delivers safe visibility in critical infrastructure without risking production systems. It supports insider threat detection and operates reliably in highly restricted or air-gapped setups.
Final Thoughts: Think Like a Hacker to Defend Like a Leader
As Sanjay Sengupta, CTO of WhizHack Technologies, says:
“To beat a hacker, we need to think like them - and deceive them into believing our digital vulnerabilities.”
ZeroHack TRACE transforms your IT and OT environment into an intelligent hunter’s maze. It actively guides attackers into controlled deception layers while giving your security team valuable and actionable intelligence.
In an era of advanced persistent threats, traditional defense is no longer enough.
“Active deception is becoming the gold standard”
Ready to Strengthen Your Security Posture?
See active deception technology in action in your environment.